

OpenCloud
Docker app from junkerderprovinz's Repository
Overview
Readme
View on GitHub
Build Lint Docker Pulls Image Size Arch OpenCloud Unraid License: AGPL-3.0
A plug-and-play Docker image that turns the official OpenCloud server into a genuine
one-click Unraid app: it runs the required first-boot init for you, heals the
appdata permissions and honours Unraid's PUID/PGID. No console,
no chown, no config-file editing required.
[!IMPORTANT] Keep every OpenCloud folder off
/mnt/user. OpenCloud has no database and writes its metadata and message bus as files all the time. Through Unraid's share layer a large sync can hang that layer, and with it every container on/mnt/user, until you reboot. Give Config and Data the SSD pool itself and Files a single array disk.



))
))
))
))
))

A one-knight job: I build it, keep it running, work through the issues and add what people ask for, until nothing is missing. It is free, with no accounts, no telemetry, no ads and no paid tier. No asterisk anywhere. Nothing readable ever leaves your own walls. Forged on evenings and weekends, with heart and stubbornness.
If it has earned a place on your server or computer, toss a coin to your knight: it helps cover the costs and keeps the project alive. It also makes this knight's heart beat a little faster. Three ways below, whichever suits you.
))
))
))

The files and documents in these pictures are made up.
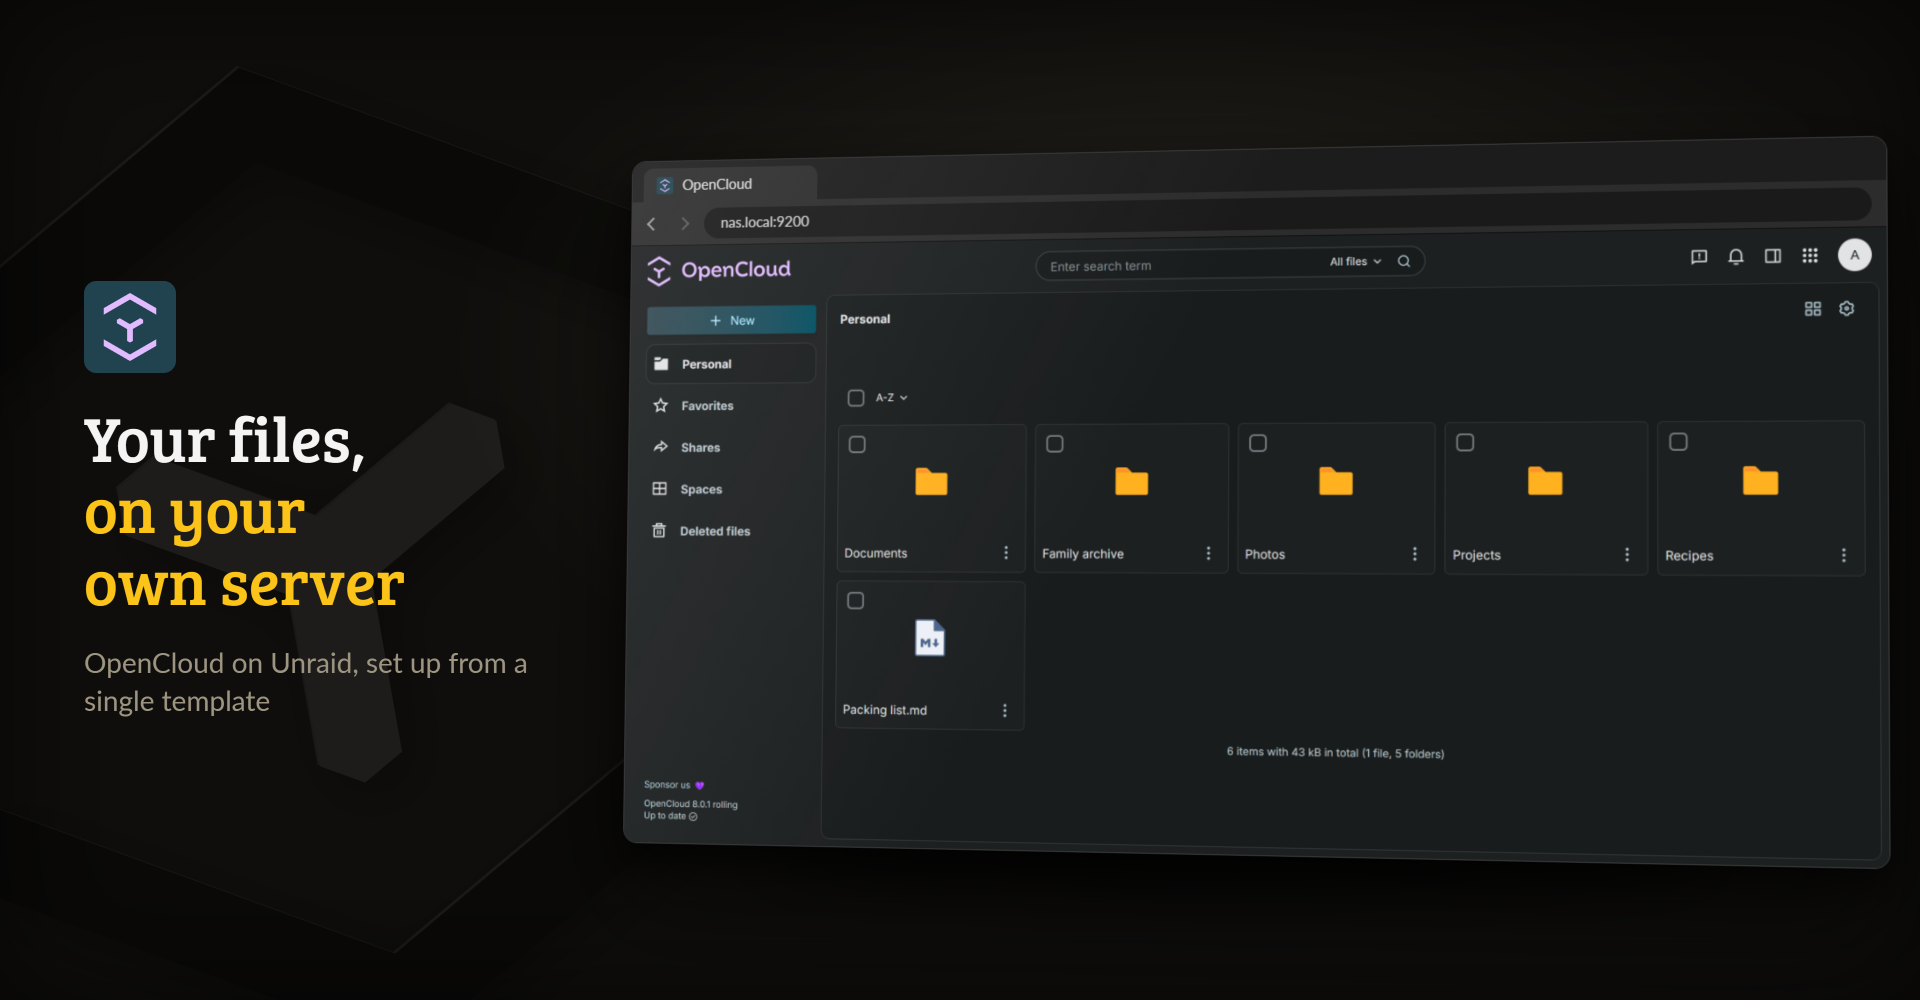
Your personal space in OpenCloud, in any browser on your network
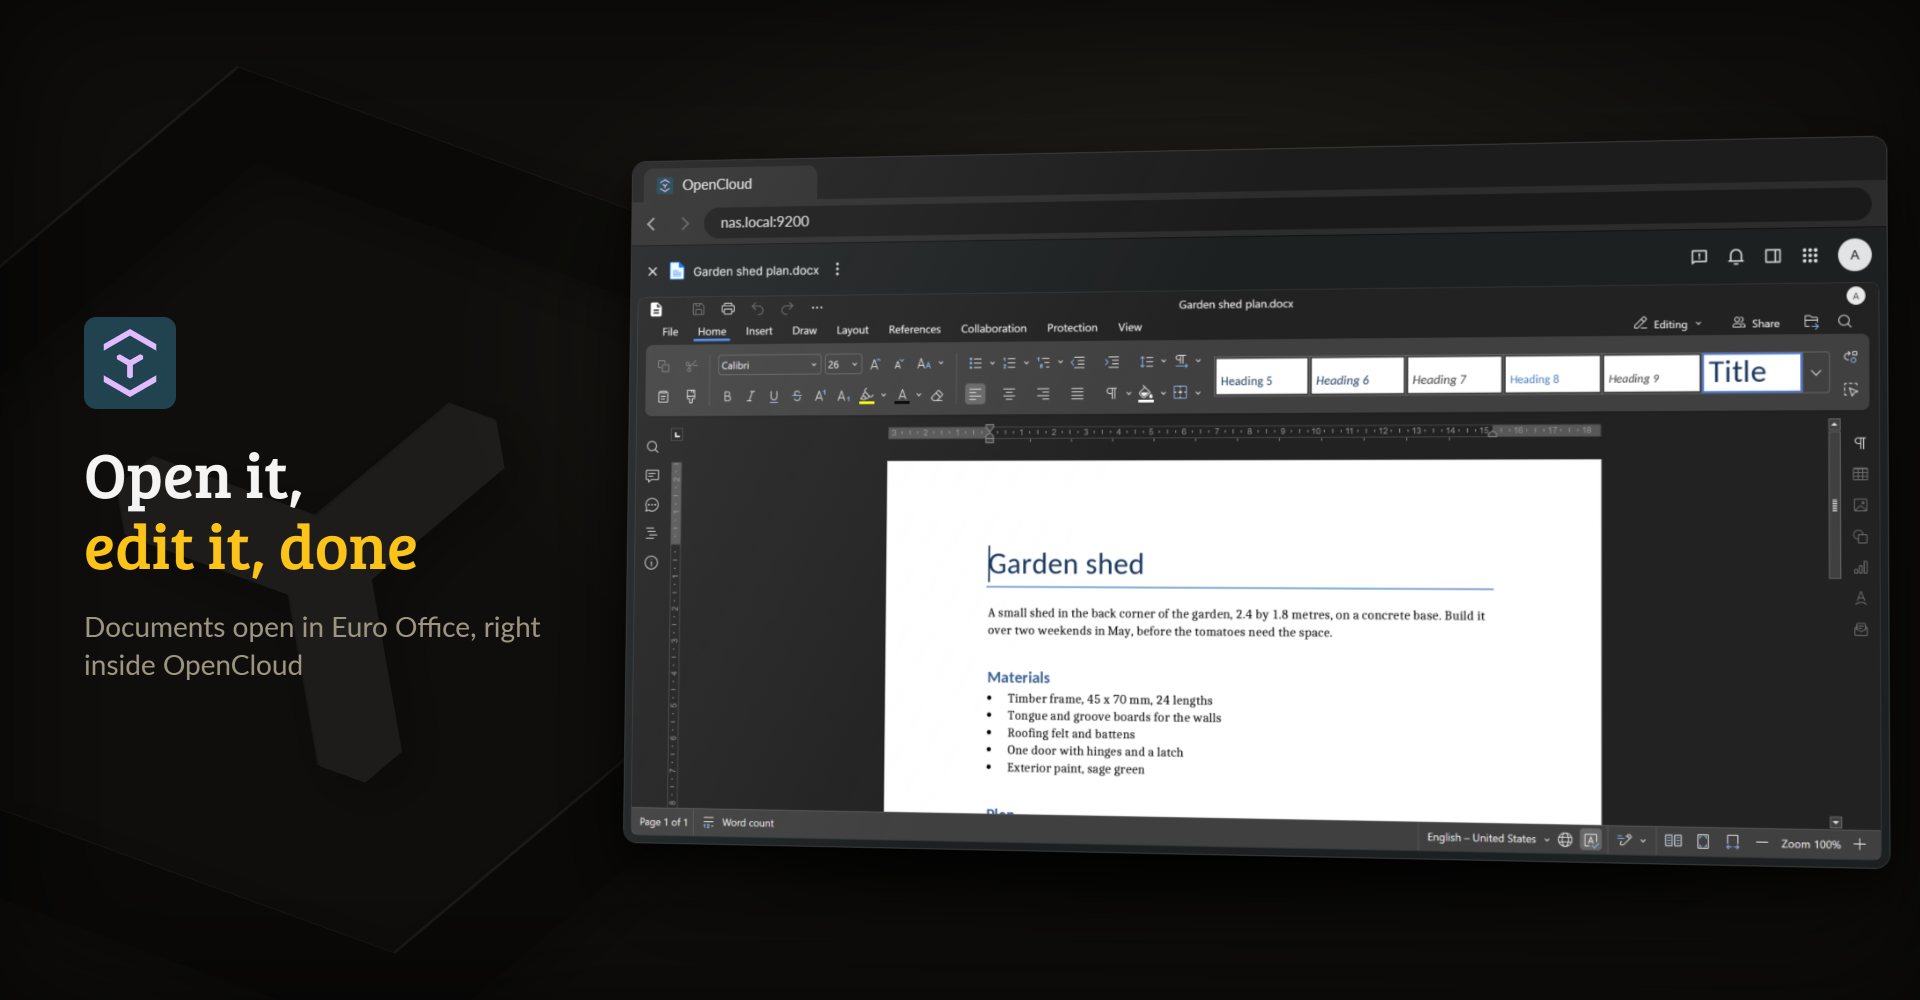
Office files open in Euro Office, right inside OpenCloud

OpenCloud is a self-hosted file sync and share platform from the ownCloud Infinite Scale family. The official opencloudeu/opencloud image runs as a fixed user without PUID/PGID, so on Unraid's root-owned folders the first start fails with "permission denied", and it needs opencloud init run by hand. This image is the unmodified upstream one with a small entrypoint in front:
- Starts on the first try. It runs
opencloud initonce, hands the config and data folders toPUID:PGID(Unraid'snobody:usersby default) and drops to that user. - Two channels.
:rolling, the template default, follows OpenCloud's newest releases, and:productionits production line. Both are rebuilt every week, for amd64 and arm64.:latestis the production line at this image's newest release. - Web office in three fields. Pick Euro Office, Collabora or OnlyOffice, and the container wires up OpenCloud's collaboration service, the proxy routes and the Content-Security-Policy. Euro Office runs under OpenCloud's own address, so it needs no certificate of its own.
- Files apart from Data. An optional Files path keeps your files on an array disk while the message bus, search index and accounts stay on a fast pool. The log warns at startup when either path goes through Unraid's share layer.
- A search index that cannot stop the server. An index OpenCloud could not open is moved aside before the start and rebuilt in the background.
- Branding, if you want it. An optional app lets admins set the name, slogan, logos, favicon and login background from the web interface.

- Install OpenCloud from Community Applications.
- Set Admin Password, and set Public URL to the address clients use, for example
https://192.168.1.10:9200. It has to be https, and Unraid does not fill it in. - Set Config, Data and, if you need it, Files before the first start, as described in Where Config, Data and Files go.
- Click Apply and wait for
OPENCLOUD IS READYin the log. Then open the Public URL, accept the self-signed certificate once and sign in asadmin.
Without Unraid:
docker run -d --name opencloud \
  -p 9200:9200 \
  -e IDM_ADMIN_PASSWORD='change-me-please' \
  -e OC_URL='https://192.168.1.10:9200' \
  -e OC_INSECURE=true \
  -v /path/to/config:/etc/opencloud \
  -v /path/to/data:/var/lib/opencloud \
  --restart unless-stopped \
  junkerderprovinz/opencloud:rolling
Editing documents. Install Euro Office and set its JWT secret. Here, set Web office suite to euro-office, Office document server URL to the address its WebUI button opens, such as http://192.168.1.10:9900, and Office WOPI secret to the same text as that JWT secret. Collabora and OnlyOffice load the editor straight from their own server, so for them the URL has to be https.
Behind a reverse proxy that terminates TLS, set PROXY_TLS=false, OC_URL to the external address and OC_INSECURE=false, and point the proxy at port 9200.
Configuration, Files and S3, the web office, the reverse proxy, updating and troubleshooting are explained step by step in the guide.
Other Docker hosts
compose.yaml runs OpenCloud on any Linux server with Docker. Put it in a folder of its own, fill in every value marked required and start it with docker compose up -d. The folders are created next to the file.
- Synology: in Container Manager, create a project from the file (DSM 7.2 or newer).
- Proxmox: run it in a VM or an LXC container that has Docker.
- MOS: install OpenCloud from the MOS Hub.
- ZimaOS and CasaOS: add the community store and install OpenCloud from it.
One knight builds this, and AI is one of the tools I work with, the same way I work with an editor or a compiler. It helps me write code and documentation and it checks my work, and that saves me a good many evenings. It does not make the decisions, though. I read and understand everything before it ships, and if something here breaks, that is on me and not on the tool.
You do not have to take my word for it. The code is open and every release note is written by hand. The issue tracker shows how problems actually get handled, including the ones I got wrong the first time. If you find something that is not right, open an issue and I will look at it.
Questions? Check the support thread. Bugs, ideas or feature requests? Please open a GitHub issue.
The AGPL-3.0 covers this wrapper only. OpenCloud and the bundled gosu are Apache-2.0, see NOTICE. The OpenCloud logo and wordmark belong to OpenCloud GmbH and are used unmodified to name the upstream project. This packaging is not affiliated with or endorsed by OpenCloud GmbH.
Categories
Download Statistics
Total Downloads Over Time
Related apps
Explore more like this
Explore allLinks
Details
junkerderprovinz/opencloud:rollingRuntime arguments
- Web UI
https://[IP]:[PORT:9200]/- Network
bridge- Shell
sh- Privileged
- false
- Extra Params
--restart=unless-stopped
Template configuration
HTTPS port of the OpenCloud WebUI / API (self-signed cert by default). Open https://[IP]:9200 and accept the certificate once.
- Target
- 9200
- Default
- 9200
- Value
- 9200
Persistent OpenCloud configuration (opencloud.yaml and generated secrets), created on the first start. Like Data, best given as the pool path itself, for example /mnt/cache/appdata/opencloud/config.
- Target
- /etc/opencloud
- Default
- /mnt/user/appdata/opencloud/config
- Value
- /mnt/user/appdata/opencloud/config
Persistent OpenCloud data: file-tree metadata, the search index, the internal NATS message bus and transient upload staging (plus your files, unless you set Files below or use an S3/decomposeds3 backend). It writes to disk all the time, so keep it on an SSD or NVMe pool and give the pool path itself, for example /mnt/cache/appdata/opencloud/data. The /mnt/user/appdata default goes through Unraid's share layer unless appdata is an exclusive share, and a large sync can hang that layer until the server is rebooted. If your SSD is too small for all your files, set Files below to a single array disk and leave Data here.
- Target
- /var/lib/opencloud
- Default
- /mnt/user/appdata/opencloud/data
- Value
- /mnt/user/appdata/opencloud/data
Optional: where your files are stored, for example a single array disk such as /mnt/disk1/opencloud/files. Give the disk itself, not a /mnt/user share: a large sync can hang the share layer and every container on it. Left empty, the files stay inside Data. Set it when Data is on a small SSD or cache pool: the files then go here, and Data keeps only the message bus, search index and accounts, the parts that write to disk all the time and stall on the array. Set it before the first start. Added to an install that already has files, it starts with an empty folder and the old files stay in Data until you move them over (guide, 'Files in a separate folder').
- Target
- /files
Password for the built-in 'admin' user. REQUIRED. Applied on the first start (during init). Choose a strong value - this is the login for your whole cloud.
- Target
- IDM_ADMIN_PASSWORD
REQUIRED. The URL clients use to reach OpenCloud, and the login (OIDC) issuer. Unraid does NOT auto-fill this: replace YOUR-SERVER-IP with your Unraid server's LAN IP, e.g. https://192.168.1.10:9200 (keep the https:// and the :9200 port). Behind a reverse proxy set your external https URL instead, e.g. https://cloud.example.com. Must be https. If you leave the placeholder, the container falls back to its own IP so it still boots, but client logins may not work until you set the real address.
- Target
- OC_URL
- Default
- https://YOUR-SERVER-IP:9200
- Value
- https://YOUR-SERVER-IP:9200
'true' (default) accepts the container's self-signed certificate - correct for a direct Unraid install. Set 'false' when a reverse proxy provides a valid certificate.
- Target
- OC_INSECURE
- Default
- true|false
- Value
- true
Verbosity of the container log.
- Target
- OC_LOG_LEVEL
- Default
- info|warn|error|debug
- Value
- info
'true' seeds a set of demo users (alan, mary, ...) with well-known passwords - handy for testing, unsafe for real use. Keep 'false' for a real deployment.
- Target
- IDM_CREATE_DEMO_USERS
- Default
- false|true
- Value
- false
'true' (default) = OpenCloud serves HTTPS itself on 9200 (self-signed) - correct for a direct Unraid install. Set 'false' when a reverse proxy terminates TLS in front of the container; then also set the Public URL to your external https URL and 'Allow self-signed TLS' to 'false'.
- Target
- PROXY_TLS
- Default
- true|false
- Value
- true
'true' lets a WebDAV client sign in with a username and an APP TOKEN, created under Account -> App tokens in the web interface. rclone, phone sync apps and anything else that cannot do the browser sign-in need this; without it every such request is refused with 401 before the token is even read, which looks exactly like a wrong token. It does NOT enable the account password for WebDAV - that is the separate PROXY_ENABLE_BASIC_AUTH, which stays off. A token can be revoked on its own, without changing the account password.
- Target
- PROXY_ENABLE_APP_AUTH
- Default
- false|true
- Value
- false
'false' (default) = no Branding app. 'true' adds one to the web interface, where accounts with the Admin role set the instance name, slogan, logo (plus one for dark mode), favicon, login background and whether the sign-in card is light, dark or follows the browser; other accounts do not see it, and the small service behind it (proxy route /brandingsvc/) checks every change with OpenCloud and refuses theirs. The name shows in the browser tab and on the login page, the slogan on the login page and on public link pages. Saved changes apply without a restart, on the login page too; only switching this setting needs one. Switching back to 'false' removes the app and keeps the saved branding, but on the login page only your logo and background remain. With your own /etc/opencloud/proxy.yaml the app turns on only if that file has the /brandingsvc/ route. With your own IDP_ASSET_PATH the login page keeps its own title, footer, favicon and card, and adding the first login background, or removing it, needs a restart. See the README 'Branding' section.
- Target
- BRANDING_APP
- Default
- false|true
- Value
- false
User-ID OpenCloud runs as. Default 99 (nobody on Unraid). The wrapper heals appdata ownership to match on start.
- Target
- PUID
- Default
- 99
- Value
- 99
Group-ID. Default 100 (users on Unraid).
- Target
- PGID
- Default
- 100
- Value
- 100
How OpenCloud stores your files. Keep 'posix' (the default) for a normal local install - files live on the Data volume. Choose 'decomposeds3' ONLY to keep file blobs in an S3 bucket (then fill the five S3 fields below); even then the metadata tree stays on the local Data volume and must be backed up. Do NOT leave this blank and never type 'local' - both break file access (files appear but are greyed out and cannot be opened or downloaded). The driver is fixed at first start; to change it, start with a fresh Data folder.
- Target
- STORAGE_USERS_DRIVER
- Default
- posix|decomposeds3
- Value
- posix
S3 API endpoint URL. Self-hosted SeaweedFS: the internal http URL on its S3 port 8333, e.g. http://192.168.1.10:8333. Self-hosted Garage: its S3 API port 3900, e.g. http://192.168.1.10:3900. AWS/B2/Wasabi: their https endpoint. Only used when the driver above is 'decomposeds3'.
- Target
- STORAGE_USERS_DECOMPOSEDS3_ENDPOINT
Bucket region. Use 'default' for self-hosted SeaweedFS, 'garage' for self-hosted Garage (its default region), or your provider's region (e.g. eu-central-1) for AWS/B2/Wasabi. Only used with the 'decomposeds3' driver.
- Target
- STORAGE_USERS_DECOMPOSEDS3_REGION
- Default
- default|garage|us-east-1|us-east-2|us-west-1|us-west-2|eu-central-1|eu-west-1|eu-west-2|eu-north-1|ap-southeast-1|ap-southeast-2|ap-northeast-1|ca-central-1|sa-east-1
- Value
- default
Access key ID for the bucket. Self-hosted SeaweedFS/Garage: the Access Key you set on that container's template directly. AWS: an IAM access key; B2/Wasabi: an application/API key.
- Target
- STORAGE_USERS_DECOMPOSEDS3_ACCESS_KEY
The secret that pairs with the access key. Self-hosted SeaweedFS/Garage: the Secret Key you set on that container's template directly. Stored masked.
- Target
- STORAGE_USERS_DECOMPOSEDS3_SECRET_KEY
Name of the S3 bucket to store blobs in. Create it FIRST - the container does not. SeaweedFS: use its own 'Pre-create Bucket' template field. Garage: use its own 'Bucket' template field. Either way, or with any S3 tool. AWS/B2/Wasabi: create a bucket in the provider console. Enter that exact name here.
- Target
- STORAGE_USERS_DECOMPOSEDS3_BUCKET
Turns on editing documents in the browser. The editor runs as its own container, for example the Euro Office template. Choices: off, euro-office, collabora, onlyoffice. See the README section 'Web office'.
- Target
- OFFICE
- Default
- off|euro-office|collabora|onlyoffice
- Value
- off
Address of the Euro Office container on your network, the one its WebUI button opens, e.g. http://192.168.1.10:9900. OpenCloud passes the editor through its own address, so plain http works and there is no certificate to accept. For Collabora or OnlyOffice, enter their https address.
- Target
- OFFICE_SERVER_URL
The same text as the JWT secret in the Euro Office container. If they differ, documents fail with 'document security token is not correctly formed'. Collabora does not need it.
- Target
- OFFICE_WOPI_SECRET
Search inside file CONTENTS (PDF, Word, Excel, ...), not just file names. 'false' (default) = OpenCloud's normal name/metadata search. 'true' = content search via Apache Tika. Tika ALWAYS runs as a SEPARATE container that you install and point to below: install a Tika template from Community Applications (search 'Tika'), image apache/tika, port 9998 (a '-full' tag also OCRs scanned images). NOTE: only files uploaded or changed AFTER you enable this are content-indexed; existing files are not re-indexed automatically (re-upload or edit them). See the README 'Full-text search' section.
- Target
- FULLTEXT_SEARCH
- Default
- false|true
- Value
- false
Network-reachable URL of your Apache Tika container, e.g. http://192.168.1.10:9998. Only used when 'Full-text search (Tika)' is 'true'.
- Target
- TIKA_URL